Frontier AI Cyber Threats: What the New ASD and AICD Guidance Means for Australian Boards
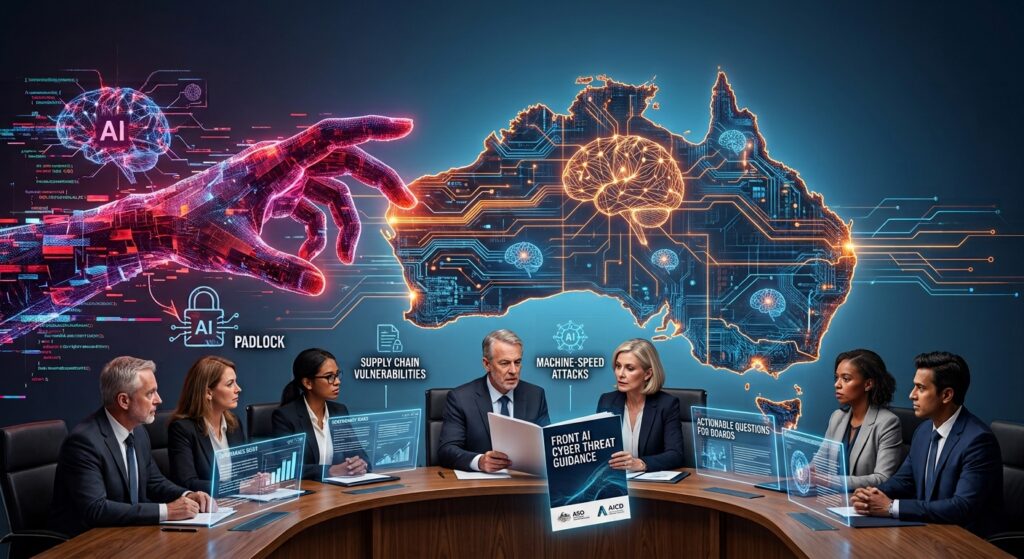
The release of the joint guidance from the Australian Signals Directorate (ASD) and the Australian Institute of Company Directors (AICD), Frontier AI Cyber Threat Considerations for Boards of Directors, marks a critical turning point for corporate governance. What the New ASD and AICD Guidance Means for Australian Boards.
Frontier AI models, characterised by advanced reasoning, automated coding, and autonomous problem-solving capabilities, are fundamentally altering the cyber threat landscape. Threat actors can now weaponise vulnerabilities at machine speed, chain together minor system flaws into major breaches, and execute attacks with minimal human oversight. For directors, this means legacy risk tolerances and slow compliance cycles are no longer fit for purpose. Cyber security is firmly a boardroom responsibility.
Key Governance Takeaways from the August 2026 Guidance
The ASD and AICD framework establishes clear threshold questions and priorities that directors must put to management:
- Challenging Vulnerability Assumptions: How quickly can your organisation identify and patch system flaws before autonomous AI tools exploit them at scale?
- Cyber Supply Chain Oversight: Do you possess absolute visibility over third- and fourth-party software suppliers, including a clear understanding of foreign ownership, control, and influence?
- Operational Resilience: Can your business maintain continuity if critical governance systems face continuous, automated, and targeted disruption?
Governance Technology as a Frontline Defense
In an era where software supply chains are heavily targeted by automated threats, the tools boards use to communicate must represent the highest standard of resilience. Choosing a secure board portal is no longer just about convenience or paperless efficiency; it is an active exercise in risk mitigation.
As a best-practice example, Athena Board demonstrates how an Australian-owned governance platform aligns directly with the security expectations reinforced by the ASD and AICD. Built with a zero-trust architecture and proprietary encryption mechanisms (such as zero-knowledge Lockbox technology), the platform ensures that sensitive board papers and strategic communications remain entirely encrypted, meaning even internal system administrators cannot read them.
By maintaining rigorous, independently audited frameworks like ISO 27001 alongside specialised local educational standards like ST4S, Athena Board removes the guesswork from third-party vendor oversight. It provides directors with the absolute assurance that their most confidential discussions are shielded from both human and agentic AI-driven threats.
Next Steps for Directors
The window to adapt to agentic, machine-speed cyber attacks is measured in weeks or months, not years. Directors must move beyond passive compliance, rigorously test their digital supply chains, and demand certified, secure-by-design infrastructure for every corner of the boardroom.
Athena Board can help, contact us at sales@athenaboard.com or start your trial at www.athenaboard.com.