Why ISO 27001 Certification Matters for Your Board Portal
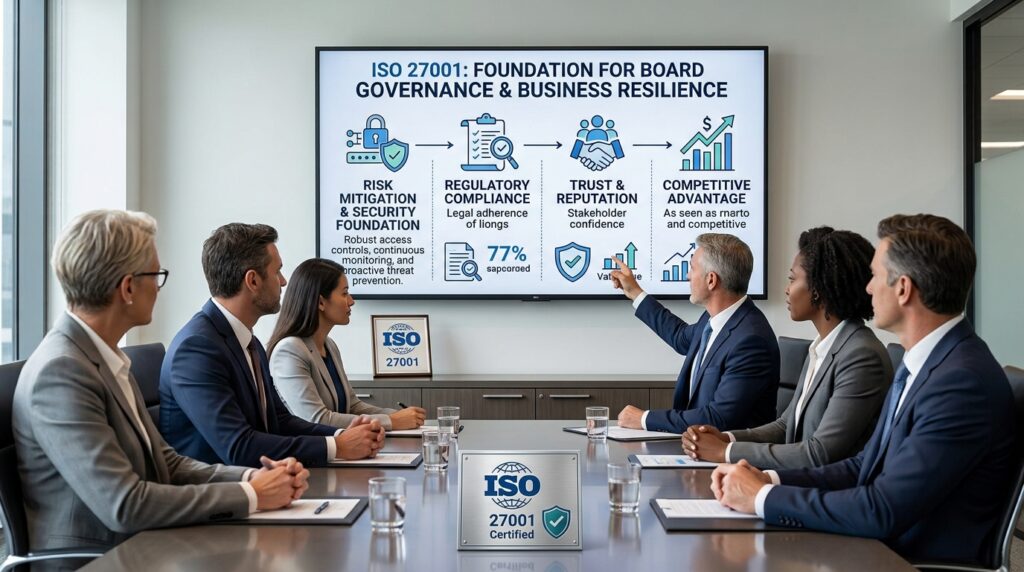
Corporate governance relies heavily on trust, confidentiality, and integrity. When boards meet to discuss sensitive mergers, financial results, or strategic pivots, the documentation they share represents some of the most critical intellectual property and market-sensitive data an organisation holds. Despite this, many groups still rely on fragmented communication channels or unverified software solutions – Why ISO 27001 Certification Matters.
Decoding ISO 27001 in Modern Governance
ISO 27001 is the internationally recognised gold standard for information security management systems (ISMS). Achieving this certification requires an organisation to undergo a rigorous, independent audit of its security controls, risk management framework, and operational protocols.
For a board portal, ISO 27001 is far more than just a marketing badge or a tick-box compliance exercise. It provides a formal guarantee that a vendor treats data protection as a continuous, systemic discipline rather than an afterthought. It dictates how code is deployed, how access is restricted, and how vulnerabilities are identified and neutralised.
The Direct Bridge: From Internal Processes to Product Security
It is a common misconception that software security is purely about robust firewalls and complex encryption algorithms. In reality, a software product is only as secure as the internal processes of the company that builds and maintains it.
- Rigorous Access Controls: ISO 27001 mandates strict role-based access management internally. This operational discipline translates directly into features like multi-layered authentication and granular permission settings within the portal, ensuring only authorised directors view sensitive files.
- Secure Development Lifecycles: Certified ISMS frameworks require continuous code reviews and vulnerability testing. This guarantees that new features, such as AI-driven document summaries or real-time collaboration tools, do not inadvertently introduce security backdoors.
- Incident Management Protocols: Certification forces organisations to establish clear, tested playbooks for anomaly detection and breach response. If an unexpected event occurs, structured protocols ensure rapid containment long before stakeholders are compromised.
Tailoring Board Portal Security Across Different Sectors
Different types of organisations face unique threat landscapes, regulatory obligations, and risk profiles. While the core mandate of protecting sensitive information remains universal, the practical implications of adopting an ISO 27001-certified platform like Athena Board vary significantly across sectors.
Corporate Entities
ASX-listed companies and large enterprises operate under intense regulatory scrutiny from bodies like ASIC, alongside strict market disclosure rules.
- Market-Sensitive Data: Corporate boards routinely handle confidential M&A discussions, earnings previews, and executive compensation data. A leak can trigger catastrophic share price volatility or insider trading investigations.
- Supply Chain and Investor Pressure: Institutional investors increasingly mandate robust cybersecurity frameworks as part of their environmental, social, and governance (ESG) due diligence. Using an ISO 27001-certified portal assures stakeholders that enterprise risk management extends directly to board-level communications.
Small and Medium Enterprises (SMEs)
SMEs often operate with lean administrative teams and limited dedicated IT security personnel, making them prime targets for opportunistic cybercriminals.
- Resource Constraints: Because SMEs rarely have the budget to build custom security operations centres, they must rely on out-of-the-box trust.
- Operational Continuity: A targeted ransomware attack or data breach can cripple an SME’s cash flow and reputation permanently. An ISO 27001-certified portal provides enterprise-grade infrastructure out-of-the-box, allowing smaller businesses to secure their governance without scaling internal IT overheads.
Not-for-Profits (NFPs)
NFPs operate on tight budgets while managing high-trust environments involving donor databases, government grants, and vulnerable community stakeholders.
- Reputational Risk: Public trust is the primary currency for any NFP. A data breach involving donor or beneficiary information can instantly devastate public confidence and fundraising efforts.
- Accountability: NFP board members are often volunteers carrying personal fiduciary liabilities. Utilising a certified governance tool minimises their personal exposure and demonstrates rigorous stewardship of organisational resources to philanthropic partners.
Schools and Educational Institutions
Independent schools, universities, and educational governing bodies manage highly sensitive compliance frameworks, student records, and staff details.
- Specialised Compliance: In Australia, educational boards must align with stringent frameworks like the Safer Technologies for Schools (ST4S) initiative alongside standard privacy legislation.
- Protecting Minors and Staff: Educational governance involves safeguarding minors’ data alongside delicate operational reviews. Athena Board’s dual alignment with ISO 27001 and ST4S makes it a tailored fit for school councils, ensuring absolute compliance with child safety and data protection mandates.
How does your current board management approach address the specific compliance requirements of your sector?
Athena Board: A Benchmark for Certified Security
As an Australian-owned governance platform, Athena Board demonstrates how formal certification shapes a secure, high-performing product. Built with a zero-trust architecture utilising advanced encryption layers (such as their proprietary Lockbox solution), the platform ensures that data remains fully encrypted at rest, in transit, and on end-user devices, meaning not even internal system administrators can decrypt board materials
By maintaining formal ISO 27001 certification alongside targeted compliance standards like the Safer Technologies for Schools (ST4S) assessment, Athena Board bridges the gap between high-level compliance mandates set by bodies like ASIC and everyday usability. It proves that rigorous internal security processes do not have to come at the expense of a clean, intuitive user experience.
Moving Forward
When evaluating governance technology, directors and company secretaries must look past surface-level feature lists. Asking whether a platform is ISO 27001 certified cuts straight to the core of the matter, offering definitive proof that the vendor’s internal operations match the security promises they make to the boardroom.
Athena Board can help, contact us at sales@athenaboard.com or start your trial at www.athenaboard.com.